Built by people who know the audit gap firsthand
We started PCIOasis because annual QSA visits leave merchants exposed for 11 months. Continuous monitoring closes that gap.
Close the 11-month compliance gap
PCI DSS audits occur annually. Breaches and configuration drift occur continuously. Most merchants find compliance gaps only when a QSA flags them, or when a breach forces the issue.
PCIOasis connects to your cardholder data environment and runs the same control checks a QSA would run, around the clock. When drift appears, you know in minutes, not months.
Our goal is to make continuous PCI compliance accessible to any merchant processing card data, without a dedicated security team to interpret the standard.
Dallas, 2024
PCIOasis was founded in Dallas, Texas by two engineers with years of experience building and breaking payment infrastructure. They saw organizations treat PCI as a once-a-year event, then pay through repeat findings, re-audits, or worse. They built the tool they wished existed for teams processing card data without dedicated compliance engineering resources.
We are a small team focused on one goal: giving payment teams a real-time view of PCI compliance posture, not a snapshot from a year ago.
The team behind PCIOasis
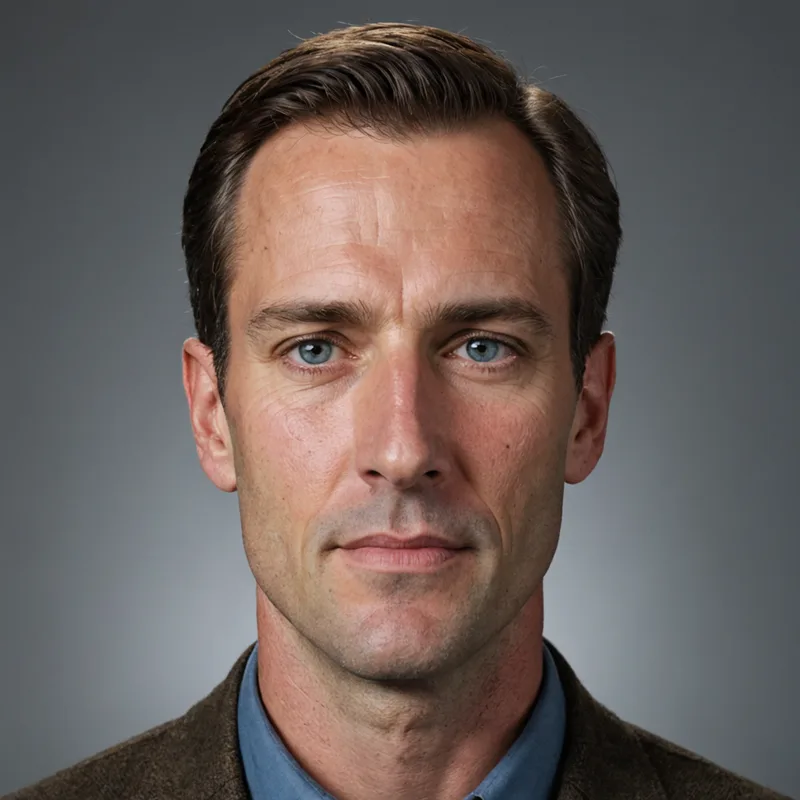
Kesten Broughton
Kesten Broughton, CEO and Co-Founder, built payment processing infrastructure and security compliance programs in high-transaction environments. After seeing the same PCI control gaps recur, he founded PCIOasis to address the tooling problem, not just the checklist.
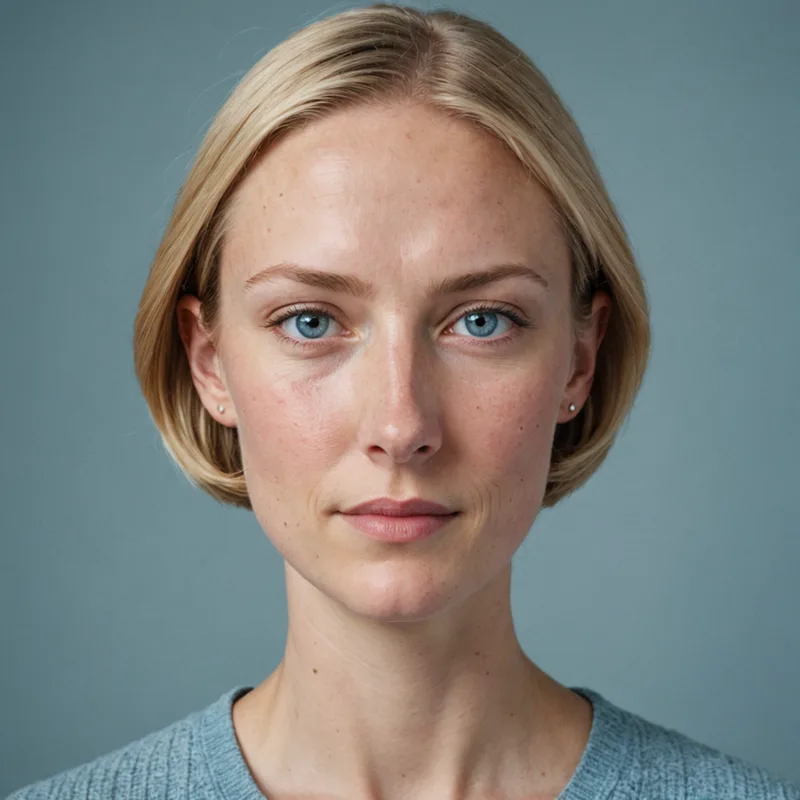
Maren Solberg
Maren Solberg, CTO and Co-Founder, has built infrastructure and security tooling for payment-adjacent systems, focusing on read-only observability that does not expand the protected attack surface. She designed the agent model and guides the technical roadmap.
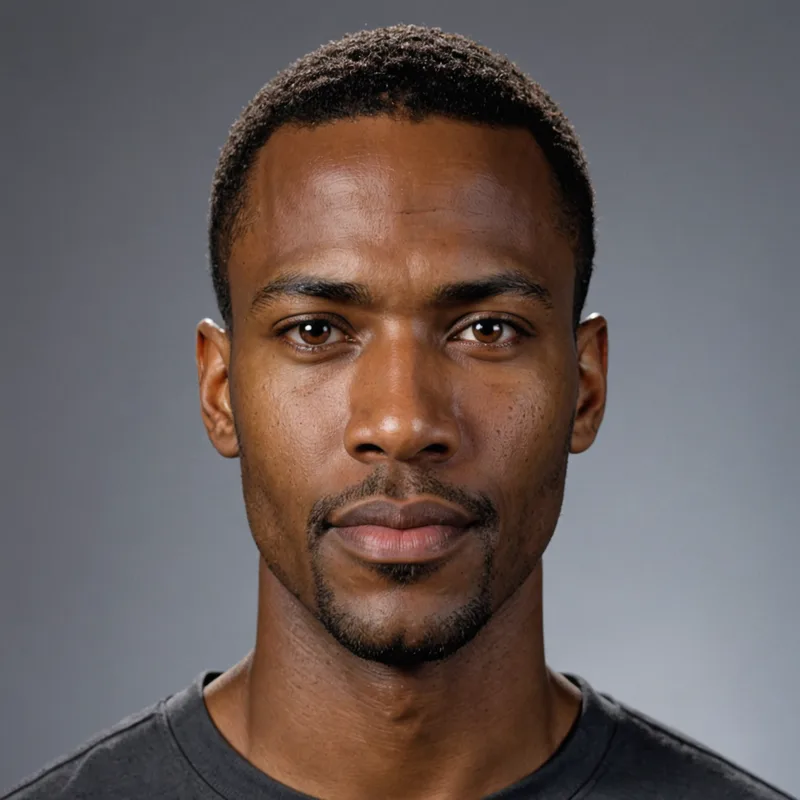
Daryl Hutchins
Daryl Hutchins, Head of Security, brings payment security consulting experience and a QSA perspective to PCIOasis. He helps ensure the product flags what a real assessor would flag and organizes evidence as audit teams expect.
What we believe about payment security
Transparency over theater
Real compliance is visible and continuous. We build tools that show what is happening in your environment, not reports designed to tell you what you want to hear on audit day.
Precision over coverage claims
We map each check to a specific PCI DSS sub-requirement, so you know exactly what you measure. We do not claim to "cover PCI" with vague dashboards.
Minimum necessary access
Our agent collects only the configuration metadata needed to test controls. We will not add data collection capabilities without a direct connection to a compliance check.
Want to learn more or work with us?
We are always glad to discuss payment security. Reach out with questions, partnership ideas, or career interest.